Understanding and Bypassing BotDeflector
The latest Queue-IT creators "innovation", or just a bunch of AI slop?

What is BotDeflector?
On a first read you may not even recognise this name, but recently lots of Queue-IT protected websites started rolling out this new captcha on either the main queue or a /softblock/ page.
By making a quick search on internet, the information about them is pretty few. You can see a totally 0 effort landing page and logo.
I honestly felt pretty ambiguous about the fact that the most famous Queue provider, used widely around ticket, sneakers and government related websites, implemented this low-effort almost inexistent captcha solution. Their website is a pure one-prompt slop with 0 effort.
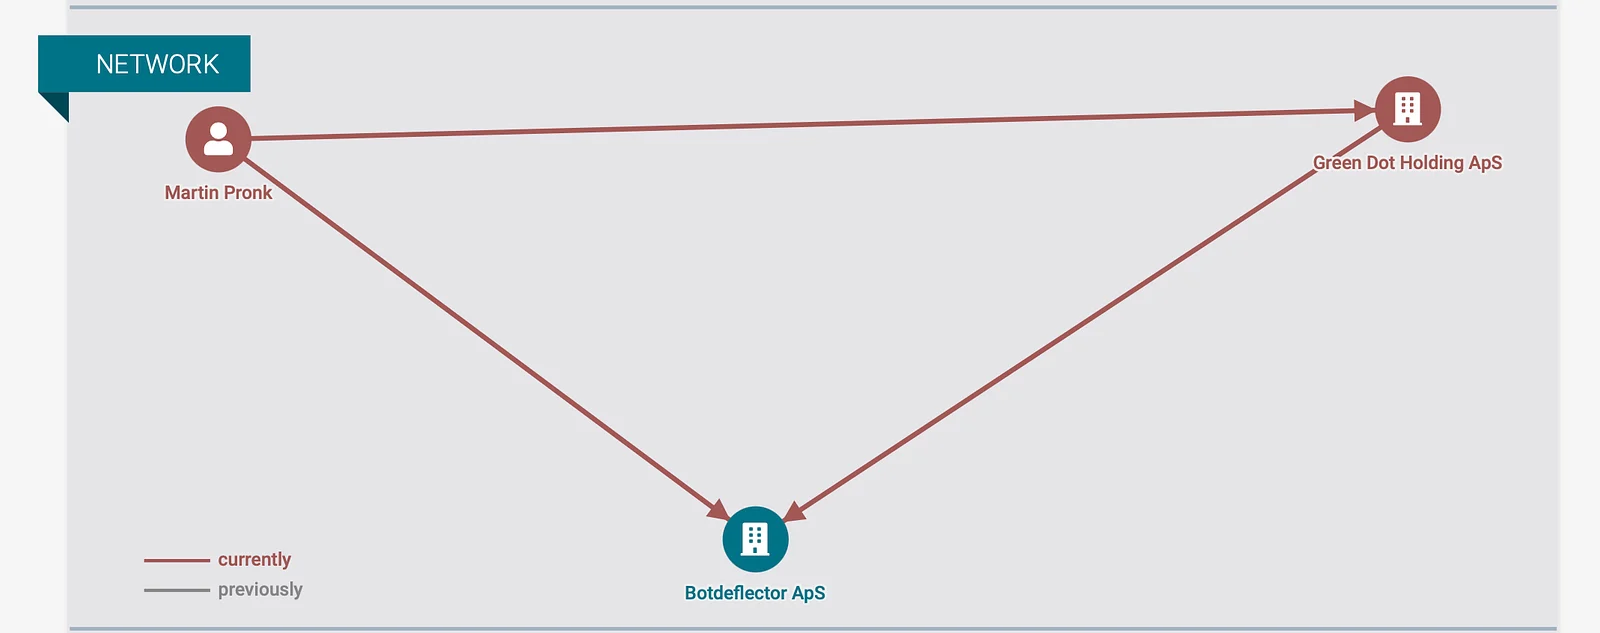
Turned out that the domain has been registered during November 2025, and the Company Owner of BotDeflector is Martin Pronk, the co-founder of Queue-IT.
Let's analyse the captcha
BotDeflector protection is based on 2 challenges.
Invisible / Proof of Work
The PoW logic comes from pow.js, obfuscated via javascript-obfuscator with string array rotation and hex accessors. The honestly most basic and low effort way to obfuscate a script.
We are not going to focus on the deobfuscation of their javascript, since I already released a repo for it.
The server gives you challenge hashes and a params blob:
{ "NODES_BITS": 12, "EDGES_BITS": 13, "CYCLE_LENGTH": 6 }
plus a GRAPH_SEED, which is your sessionId.
You build a graph where every edge index maps to two node endpoints:
h = sha256(struct.pack("<I", edge) + seed_bytes).digest()
u = int.from_bytes(h[0:8],  "little") % (1 << NODES_BITS)
v = int.from_bytes(h[8:16], "little") % (1 << NODES_BITS)
Then you find a simple cycle of length CYCLE_LENGTH and return its edgeIndices.
All the challenges in one step share the same graph. The challenge hash only picks your DFS start node:
start = int.from_bytes(sha256(bytes.fromhex(challenge)).digest()[0:8], "little") % num_nodes
Like the Queue-IT captcha, pretty simple and easy, only CPU expensive. You can find here the GO / Python / NodeJS implementation of it.
Icon Captcha
This is the only hard part of the challenge, a captcha that most of the times is hard to solve even for humans.
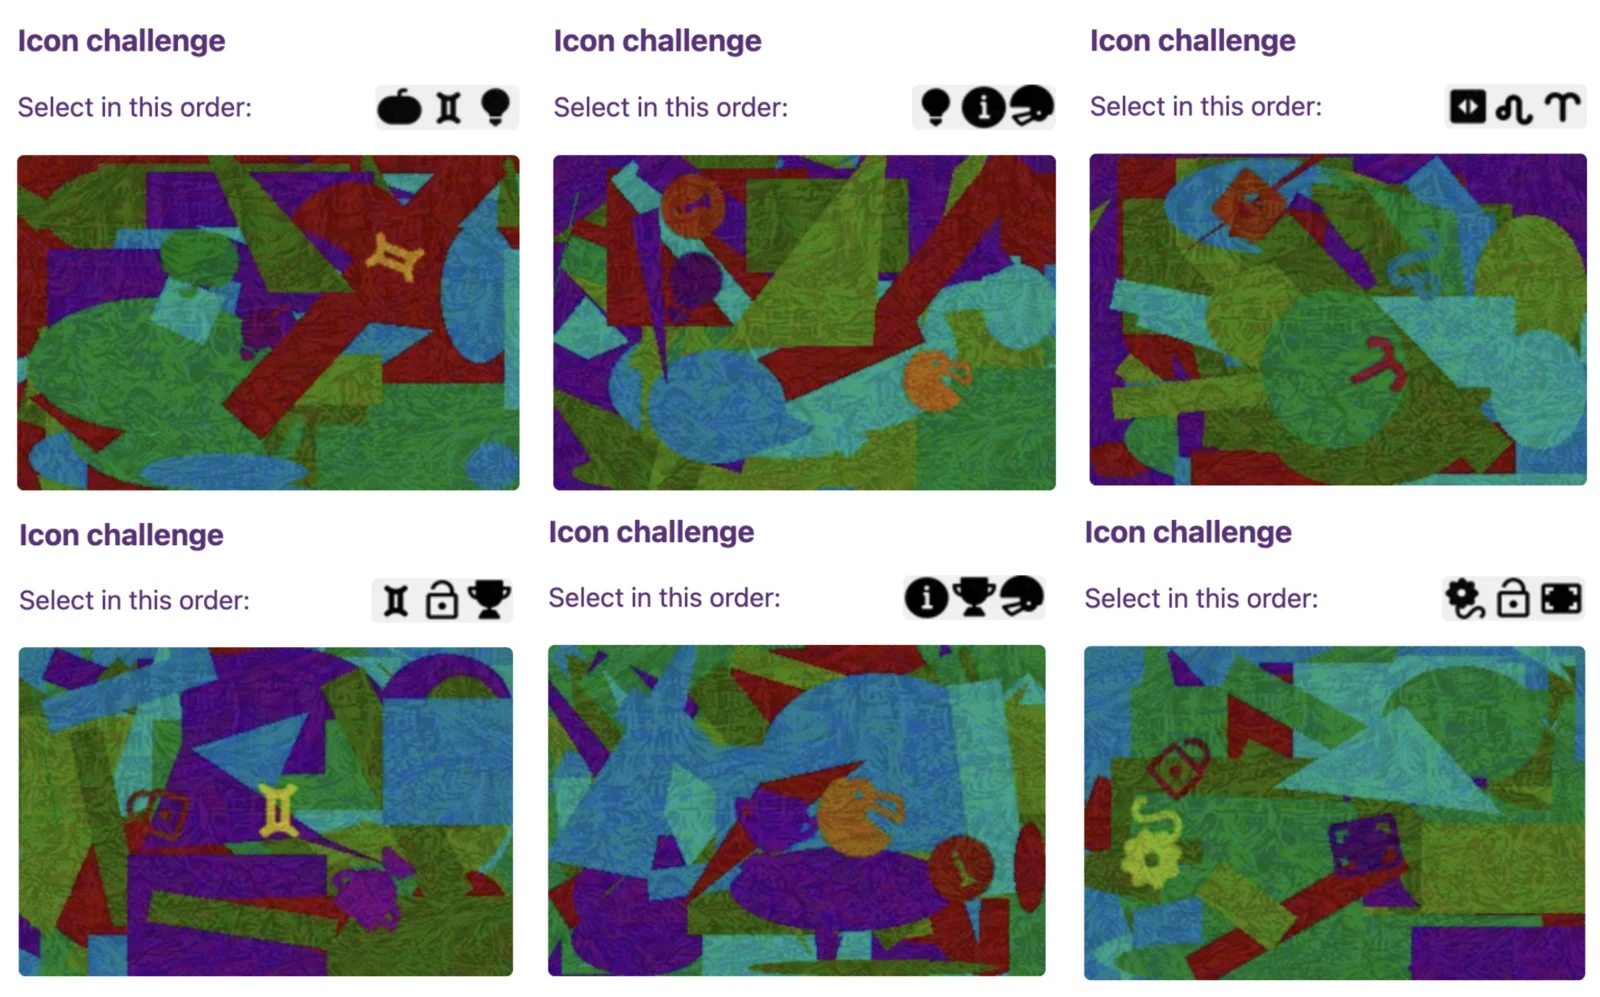
Try one yourself, it explains the difficulty faster than I can:
Try the real thing
A live BotDeflector challenge, served by the vendor. Solve it yourself and watch the flow described above run in your own browser.
Loads a third-party script from botdeflector.eu, which fingerprints your browser. Nothing is requested until you click.
And yes, that widget is running on my blog, on a domain that has nothing to do with the SiteKey it is using. There is no origin check anywhere in the flow, so you can lift a SiteKey off any protected site and serve working challenges from wherever you want. reCAPTCHA, hCaptcha and Turnstile all bind a site key to a domain allowlist, it is usually the first thing you implement. Shipping to production without it is pretty rough LOL.
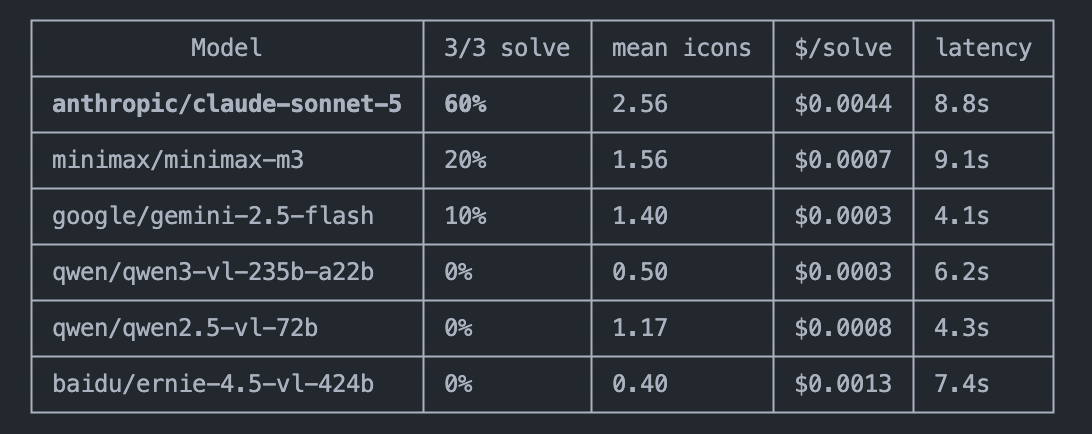
Front-tier vision models (such as GPT, Anthropic, Google ones) have a really low score rate, with the most capable one benchmarked as Claude Sonnet 5 with a 60% success rate and an obv too much cost for solving a captcha that simple. I ran this benchmark for a pure comparison human vs model, for understanding if the captchas are actually hard to understand most of the times.
So the only path forward for solving this issue has been training my own model.
Lucky the developer of this captcha didn't implement 2 important things:
- Rate limits. I can refresh and submit as much icon captchas as I want with no limits at all.
- Rejection after X tries. So I can retry solving the same image as much as I want by using the same parameters via APIs.
I didn't check for other insecurities on their endpoints, such as the possibility to solve a specific image, send empty tokens etc, but by seeing how is going it wouldn't surprise me.
Those 2 issues permitted me to have the /icon/verify endpoint as oracle. I can submit the same image until solved correctly, making it a perfect distillation for the initial versions of my model. Thanks to this I reached a 99.8% success rate for this exact kind of captcha, could have pushed it even further but I saw no need at all. All of this without having to use a single proxy, all localhost.
The Captcha Steps
Few days after the release of the captcha, their portal was live and accessible at https://portal.botdeflector.eu/ (right now returning 404).
I sadly didn't save any screenshot of it, but the main thing that you was able to do was creating captchas for testing. This internal look made me understand a bit more about the customisations they offer.
You can set up to X "steps" based on your tier. Each step can be either an invisible/PoW or icon captcha. You can also choose the difficulty of it in a scale of 1 to 5. On the PoW side the computation gets more CPU-intensive, while the icon captcha didn't seem to change much.
GDPR Compliant
The biggest claim of this captcha solution is that they are GDPR compliant.
Honestly talking the GDPR is pure bullshit. What I'm assuming is just that someone is trying to get some European funds with a project developed in an afternoon, since they can prove that is used by already hundreds of thousands of websites across the web.
Anyway by analysing the source code there are 2 issues that didn't make it GDPR compliant. They use FingerprintJS in order to fingerprint your browser:
- Canvas fingerprint (
toDataURL) requires consent, as Art. 5(3) and the ICO guidance - Audio / WebGL / font / hardware fingerprint requires consent, as EDPB 2/2023
- No transparency notice on the anti-bot flow (usually host-side), as Art. 13
Also the captchas are "hard" to solve for a normal person most of the times, requiring different retries most of the times. A colorblind or partially blind person is totally unable to solve them, not the best choice.
Conclusion
Since we are not talking about a small project/startup but a well funded company, my thoughts are more sharp. I hope to see improvements in this project and not just a quick escamotage to get european funds as Friendly Captcha has done.
Make sure to check all the repos related to this article:
Need help bypassing BotDeflector?
If you're integrating, reversing, or just trying to understand a wall, whether it's BotDeflector, a Queue-IT challenge, DataDome or Akamai, that's what we do at TakionAPI. One API call solves the full challenge flow, no browser and no need to pay for external Vision APIs/trian your ML model after a reverse engeneering work. See the BotDeflector bypass page for the endpoint. Start today with a trial
Connect with me
Sautez l'étape de la rétro-ingénierie.
Takion renvoie des cookies, en-têtes et tokens frais pour tous les grands murs antibot. Un seul POST, aucun navigateur, premier appel dans l'heure.